HIPAA Security Risk Assessment
Get a clear view of the risks affecting your healthcare IT environment. We assess systems, applications, users, and processes handling PHI and ePHI to identify vulnerabilities and compliance gaps.
Home / HIPAA Compliance Services
NG Cloud Security provides HIPAA compliance services to help healthcare organizations and businesses handling protected health information strengthen security and reduce compliance risks. Our experts assess your IT environment, identify security gaps, and implement safeguards for PHI and ePHI across identities, endpoints, applications, Microsoft 365, Azure, and cloud infrastructure.
Our HIPAA compliant IT services support healthcare providers, HealthTech companies, business associates, medical billing organizations, and technology providers serving the US healthcare industry. From HIPAA risk assessments and data protection to access controls, security monitoring, and remediation, we help organizations build a stronger, more secure, and compliance ready healthcare IT environment.
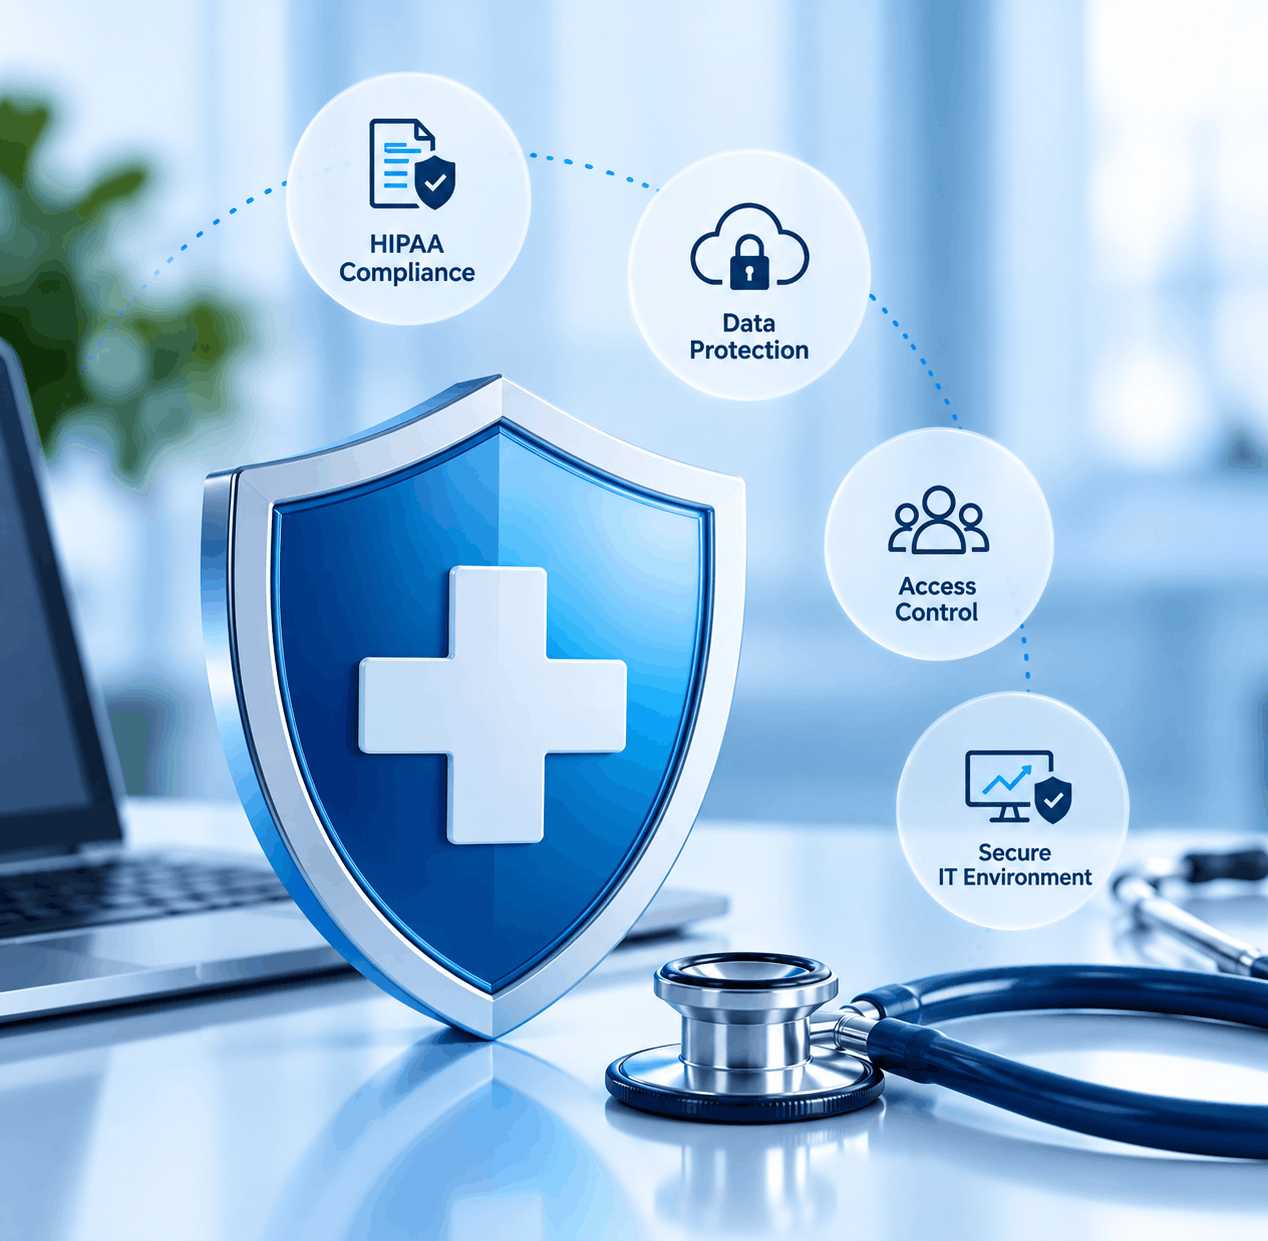
Protect sensitive healthcare data, strengthen your security controls, and address compliance gaps with practical HIPAA compliance services built around your technology environment. From risk assessment and PHI protection to Microsoft cloud security and ongoing support, NG Cloud Security helps healthcare organizations build a stronger, compliance ready IT environment.
Get a clear view of the risks affecting your healthcare IT environment. We assess systems, applications, users, and processes handling PHI and ePHI to identify vulnerabilities and compliance gaps.
Understand where your current safeguards may fall short. We review administrative, physical, and technical security controls and provide practical recommendations to improve HIPAA compliance readiness.
Protect sensitive healthcare information wherever it is stored, accessed, or transmitted. We evaluate encryption, data access, sharing, storage, and controls designed to reduce unauthorized PHI exposure.
Build security into the technology your organization uses every day. We strengthen identities, endpoints, applications, cloud services, and other critical components of your healthcare IT environment.
Secure healthcare workloads across Microsoft environments. We help strengthen identity, endpoint, data, and threat protection controls across Microsoft 365 and Azure.
Be prepared before a security incident affects sensitive healthcare data. We assess detection and response processes and help strengthen workflows for potential PHI exposure and cybersecurity incidents.
Make sure the right people have the right level of access to sensitive healthcare systems and data with stronger authentication, authorization, and identity security controls.
Finding security gaps is only the beginning. Our HIPAA compliance support helps your team prioritize remediation and strengthen technical safeguards based on identified risks.
HIPAA security is not a one time exercise. We continuously review security controls as technology and risks evolve and provide guidance to maintain a resilient, compliance ready environment.
HIPAA compliance services from NG Cloud Security help healthcare organizations protect PHI and ePHI while strengthening the technical controls supporting their compliance programs. We assess security risks across identities, endpoints, applications, Microsoft 365, Azure, and cloud infrastructure, then provide prioritized guidance for addressing identified gaps.
Our approach covers access control, data protection, encryption, security monitoring, endpoint protection, incident preparedness, and cloud security. We support healthcare providers, HealthTech companies, business associates, medical billing organizations, and Indian technology providers serving US healthcare organizations.
By combining compliance focused assessments with practical cybersecurity implementation, our HIPAA compliant IT services help organizations reduce risk, improve visibility, strengthen safeguards, and maintain a more secure healthcare technology environment as regulatory and business requirements evolve.
NG Cloud Security supports organizations that handle, process, store, or provide technology services involving PHI and ePHI, including:
Strengthen safeguards protecting patient information across endpoints, identities, applications, and cloud infrastructure.
Build stronger security controls into platforms and environments supporting US healthcare customers.
Protect PHI across billing workflows, workforce access, Microsoft 365, endpoints, and cloud systems.
Assess security risks and strengthen safeguards for organizations providing services to HIPAA regulated healthcare entities.
Discover vulnerabilities, weak controls, and security gaps that could increase risks to PHI and healthcare systems.
Strengthen safeguards around sensitive healthcare data across identities, endpoints, applications, and cloud environments.
Reduce exposure to evolving cyber threats through stronger technical safeguards and security focused remediation.
Improve alignment between your security controls, risk management practices, and applicable HIPAA requirements.
Prioritize remediation efforts and reduce the likelihood of unauthorized access, data exposure, and security incidents.
Continuously strengthen healthcare security controls as technologies, threats, and compliance requirements evolve.
HIPAA compliance services help organizations evaluate and strengthen the administrative, physical, and technical safeguards used to protect protected health information. Services may include security risk assessments, gap analysis, access control reviews, data protection, cloud security, endpoint security, incident response planning, remediation, and ongoing security support.
NG Cloud Security focuses particularly on the cybersecurity and IT controls organizations use to protect PHI and ePHI across modern technology environments.
HIPAA requirements can apply to covered entities and business associates that create, receive, maintain, or transmit protected health information in circumstances covered by HIPAA. This can include healthcare providers, health plans, healthcare clearinghouses, and certain vendors supporting them.
Technology companies, medical billing providers, HealthTech businesses, SaaS providers, and other organizations handling PHI for US healthcare customers may therefore need appropriate security and compliance controls.
Yes. NG Cloud Security can assess and strengthen security controls across Microsoft 365 and Azure environments used by healthcare organizations.
Depending on your environment and requirements, this can include Microsoft Entra ID, multifactor authentication, Conditional Access, Microsoft Purview, data loss prevention, Microsoft Defender, endpoint protection, encryption, logging, monitoring, and other security configurations designed to reduce risks to PHI and ePHI.
Location alone does not determine whether HIPAA obligations apply. An Indian company working with a US covered entity may have HIPAA related contractual and regulatory responsibilities when it performs functions involving PHI as a business associate or subcontractor.
Medical billing companies, healthcare BPOs, HealthTech providers, SaaS companies, and IT service providers serving US healthcare organizations should determine their specific obligations and implement appropriate safeguards for the PHI they handle.
Yes. NG Cloud Security supports healthcare technology companies, medical billing organizations, cloud and IT providers, and other businesses that operate as business associates. We help assess and strengthen security controls protecting PHI and ePHI, including identity, access, endpoints, cloud environments, monitoring, encryption, incident preparedness, and risk management. Where Business Associate Agreements apply, organizations should ensure their contractual and operational responsibilities are addressed alongside technical security requirements.
WhatsApp Us